
Author: Geek Guy Cybersecurity Market IntelligenceClassification: Technical Reference for CISO / SecOps / Security Analysts Executive Summary This report provides a validated technical comparison of open-source local AI video and audio generation tools and models. All sources have been cross-referenced against official repositories, Hugging Face model cards, and vendor documentation. The analysis is oriented toward…
Tag: security
Competitive Reports, Cybersecurity News
AI Cybersecurity Vendors: Market Intelligence Report 2026 AI Cybersecurity Vendors: Market Intelligence Report 2026
AI Cybersecurity Vendors: Market Intelligence Report 2026 📅 Date: September 11, 2026 🔍 Source: geekguy.com technology news coverage 📊 Coverage: Google | Anthropic | OpenAI | Abnormal AI Executive Summary In early September 2026, three major AI labs — Google, Anthropic, and OpenAI — simultaneously announced “cyber” editions of their models paired with restricted-access defender…
AI, Global Security News
Rethinking MDR as Attackers and Defenders Embrace AI
For most of the past decade, managed detection and response was the answer to a real problem. Security teams couldn’t staff around the clock, couldn’t hire enough analysts, and needed someone else to handle the alert queue. MDR stepped in. It worked well enough. Until now. The threat landscape has changed faster than the MDR…
AI, Apps, Cybersecurity, Global Security News
LangGraph Flaw Chain Exposes Self-Hosted AI Agents to Remote Code Execution
Cybersecurity researchers have disclosed details of three now-patched security flaws impacting LangGraph, including a critical vulnerability chain that could result in remote code execution. LangGraph is an open-source framework created by LangChain to build complex, stateful, and multi-agent artificial intelligence (AI) agentic applications. “An SQL injection in LangGraph’s function could
AI, Compliance, Cybersecurity, Data Breaches, Endpoint, Global Security News, Network Security, Risk Management
Reinvent Launches Managed Security for MSP Partners
Reinvent Telecom has launched MyCloud Managed Security, a fully managed cybersecurity offering built to help MSPs, VARs, and resellers expand into security services without building their own infrastructure. The new service combines Guided Vulnerability Management and Managed XDR to provide continuous monitoring, threat detection and response, asset discovery, endpoint detection and response, SIEM, SOAR, dark…
Cybersecurity, Exploits, Global Security News, Government & Policy
CISA orders feds to patch actively exploited Ivanti flaw by Sunday
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) ordered government agencies to patch an actively exploited Ivanti Sentry flaw within three days, as mandated by the newly issued Binding Operational Directive (BOD) 26-04. […]
AI, Global Security News, Risk Management
How to use NIST and ISO frameworks to govern AI agents
Security leaders no longer need convincing that AI agents introduce risk. What’s missing is how to govern them once they move into production and begin operating autonomously across enterprise environments. AI agents already read sensitive documents, invoke internal APIs, trigger workflows, and make decisions that still require human judgment. From a security perspective, the most…
AI, Global Security News
ZeroFox releases AI Analytics to bring answers directly to security teams
ZeroFox launched ZeroFox AI Analytics, a new platform capability that gives security teams real-time visibility into the signals, patterns, and trends shaping their external threat landscape. ZeroFox AI Analytics gives security teams the ability to move beyond static reports and query their data in real time. Rather than waiting on manual exports or scheduled summaries,…
AI, Global Security News, privacy
Product showcase: Avast One turns scam screenshots into actionable security advice
Avast One Free combines privacy, security, identity monitoring, and performance tools in a single platform. The app is available for Windows, macOS, Android, and iOS. Checking the device for security and privacy issues After installing it from the App Store, I ran Smart Scan, which reviews device and privacy settings and identifies areas that require…
AI, Exploits, Global Security News
Google warns of active Oracle PeopleSoft exploitation campaign linked to ShinyHunters
Google warns of active Oracle PeopleSoft exploitation campaign linked to ShinyHunters. Security coverage from iTWire.
Global Security News
Japanese energy firm loses drive with data of 10.9 million clients
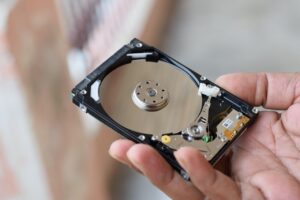
Kyushu Electric Power Co., Inc. has disclosed a physical security incident that affects private data of more than 10 million customers. […]
Global Security News
FBI shuts down 13 ‘consulting’ websites used for suspected Chinese espionage
The sites were used to lure security clearance holders into divulging classified information.
AI, Global Security News
New Attacks Trick OpenClaw AI Agent Into Running Code and Leaking Secrets
Two security teams have shown, in separate research published this week, that OpenClaw, the popular self-hosted AI agent, can be driven to run attacker-controlled code or hand over sensitive data through ordinary-looking inputs. Imperva buried instructions inside shared contacts, vCards, and location pins that the agent executed without the victim ever seeing them. Varonis built…
AI, Exploits, Global Security News
New GreatXML Exploit Bypasses Windows BitLocker via Recovery Partition XML Files
Security researcher Chaotic Eclipse (aka Nightmare-Eclipse and MSNightmare) has released a new Windows BitLocker bypass dubbed GreatXML, a day after they published an exploit for Microsoft Defender. “This was an accidental discovery, it took a total of 4 hours to find this,” the researcher said in a post on Blogger. “If you ever attempted to…
AI, Cybersecurity, Exploits, Global Security News, Government & Policy, Risk Management
CISA orders federal agencies to “patch smarter”
The US Cybersecurity and Infrastructure Security Agency (CISA) has issued a Binding Operational Directive that will change how the US federal government approaches vulnerability management. The directive arrives as the patching problem has become nearly unmanageable, driven by a surge in newly published vulnerabilities and by AI tools that are accelerating both security research and…
AI, Global Security News
The AI Exchange: Innovators in Payment Security Featuring SecurityMetrics
Welcome to the PCI Security Standards Council’s blog series, The AI Exchange: Innovators in Payment Security. This special, ongoing feature of our PCI Perspectives blog offers a resource for payment security industry stakeholders to exchange information about how they are adopting and implementing artificial intelligence (AI) into their organizations.
AI, Global Security News
Segmentation Works for OT If Operators Are Paying Attention
Operational technology security remains as difficult as ever, with even the best practice recommendation falling short.
AI, Global Security News
Why AI-driven threats are exposing the limits of MSP security stacks
AI-driven attacks are exposing the limits of fragmented MSP security stacks and slow response workflows. Kaseya breaks down why integrated security, automation, and recovery are becoming essential. […]
AI, Cybersecurity, Global Security News
Cybersecurity Stars Awards 2026: Winners Announced Across 95 Categories
Most good security work is invisible by design. Today is the exception. The 2026 Cybersecurity Stars Awards winners are announced across 95 subcategories in four main award categories. The reason is simple. Cybersecurity is full of work that deserves recognition and rarely gets it. Products that quietly close real gaps. Teams that stop incidents nobody…
Cybersecurity, Global Security News
CISA tells govt agencies to patch critical exploited flaws in 3 days
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) announced a new Binding Operational Directive, 26-04, that prioritizes security updates for Federal Civilian Executive Branch (FCEB) agencies. […]
Global Security News
New “Agentjacking” Attacks Could Hijack AI Coding Agents
Tenet Security researchers reveal how new “agentjacking” attacks could trick coding agents into executing arbitrary code
AI, Compliance, Cybersecurity, Europe, Global Security News, malware, Network Security, Risk Management
From Infosecurity Europe to CONFidence and C1b3rWall: What Security Teams Are Prioritizing in 2026
Three cities, three cybersecurity conferences, and plenty of conversations with security professionals across Europe. Over the past few weeks, the ANY.RUN team joined Infosecurity Europe in London, CONFidence Conference in Kraków, and C1b3rWall Congress in Ávila. While every event had its own focus, the discussions pointed in the same direction: security teams need faster investigations,…
AI, Apps, Global Security News, Network Security
Rubrik Q&A: New Partner Integrations, AI Solutions Launched
Recently, Rubrik, a security and AI operations company, made a series of announcements, including new partner integrations and a new agentic-first AI platform. The announcements represent Rubrik’s ongoing commitment to ensuring enterprises are agentic-ready and resilient. You can read more about the announcements here. In light of these new announcements, below is a Q&A with…
AI, Global Security News, Risk Management
Organizations can’t see much of their mobile AI activity
Organizations have limited visibility into AI activity on mobile devices despite security leaders expressing confidence in their AI governance, according to Lookout’s “Solving for the Mobile AI Blind Spot: Executive Confidence Meets Technical Reality” report. Mobile AI visibility gaps Enterprises lack visibility into a large share of mobile AI activity taking place on both corporate-owned…
AI, Global Security News
Check Point Advances Secure AI Transformation for MSPs with New Platform, AI Security Capabilities, and Unified Security Bundles
Check Point Advances Secure AI Transformation for MSPs with New Platform, AI Security Capabilities, and Unified Security Bundles. Security coverage from iTWire.
Data Breaches, Global Security News
Celebrities’ and influencers’ private communications exposed in stalkerware data breach
Celebrities’ and influencers’ private communications exposed in stalkerware data breach. Security coverage from iTWire.
Global Security News
NPM v12 to block supply-chain attacks with new security measures
The upcoming npm v12 will introduce stricter security protocols for the “npm install” command, a critical step in downloading and installing project dependencies.
AI, Cybersecurity, Data Breaches, Endpoint, Exploits, Global Security News, Government & Policy, Network Security, Risk Management
CISA tells agencies to patch smarter, not harder — foreshadowing broader industry practice
Security teams’ patching practices have come under intense pressure over the past year, as active exploitation is up, time-to-exploit windows are accelerating, and vulnerabilities have become attackers’ top initial access vector of choice. Last year, organizations fully remediated only 26% of the vulnerabilities that attackers were actively exploiting in the wild — down from 38%…
AI, Apps, Cloud Security, Cybersecurity, Global Security News, Network Security, Risk Management
News alert: Cloud security report finds fragmented tools widening the cloud complexity gap
WASHINGTON, Jun. 10, 2026, CyberNewswire–The 2026 Cloud Security Report from Cybersecurity Insiders, produced in collaboration with Fortinet, finds that 69% of organizations cite tool sprawl and visibility gaps as the top factor limiting cloud security effectiveness. Based on a survey of 1,163 IT and cybersecurity professionals, the report shows the strain: 66% lack strong confidence…
Global Security News
PCI SSC Publishes New Guidance on Compensating Controls and the Customized Approach
The PCI Security Standards Council (PCI SSC) has released a new information supplement, PCI DSS v4.x: Guidance for Compensating Controls and the Customized Approach. The document provides practical guidance to help assessed entities and assessors navigate two options in PCI DSS v4.x that provide flexibility but are often misunderstood – the use of compensating controls…
AI, Cybersecurity, Data Breaches, Exploits, Global Security News, Risk Management
CISA directive orders agencies to prioritize vulnerability patching in a new way
The Cybersecurity and Infrastructure Security Agency on Wednesday ordered federal agencies to prioritize vulnerabilities based on four criteria, as part of push to “patch smarter, not harder.” Federal agencies should emphasize patches for vulnerabilities that affect a publicly exposed asset, allow an attacker to fully automate exploitation, give attackers the ability to take over control…
Apps, Cybersecurity, Global Security News
Cybersecurity Software Fails to Detect Fifth of Brower-Based Phishing Attacks
Menlo Security research warns that as enterprise applications become increasingly browser based, traditional cybersecurity tools leave them vulnerable to cyber threats
Global Security News
ServiceNow Discloses Security Incident Exposing Customer Data
ServiceNow applied a security update after an API access issue exposed customer data, with affected firms notified through direct support cases.
Global Security News
Ivanti, Fortinet, and SAP Release Patches for Multiple Critical Vulnerabilities
Fortinet, Ivanti, and SAP have released security updates to address multiple critical security vulnerabilities that could result in arbitrary code execution and information disclosure. The security flaw patched by Fortinet relates to a command injection vulnerability in FortiSandbox, FortiSandbox Cloud, and FortiSandbox PaaS WEB UI. It’s tracked as CVE-2026-25089 (CVSS score: 9.1). “An
AI, Apps, Exploits, Global Security News
Unpatched Langflow Flaw CVE-2026-5027 Exploited for Unauthenticated RCE
A high-severity unpatched security flaw in Langflow, an open-source low-code platform to build artificial intelligence (AI) applications, has come under active exploitation in the wild, according to findings from VulnCheck. The vulnerability in question is CVE-2026-5027 (CVSS score: 8.8), a case of path traversal that could allow an attacker to write files to arbitrary locations.…
AI, APAC, Apps, Cybersecurity, Exploits, Global Security News, Network Security, Risk Management
June Patch Tuesday marks a ‘new normal’ with over 200 CVEs, 32 rated ‘critical’
June’s Patch Tuesday security updates have arrived, with SAP fixing four critical vulnerabilities and Microsoft addressing over 200 CVEs. Microsoft’s to-do list includes fixes for three zero days, 32 patches rated as ‘critical’, and a batch of other high-risk vulnerabilities that need urgent assessment. There’s also one older flaw under exploit, and some patches affecting…
Cybersecurity, Exploits, Global Security News
CISA Adds Cisco, Chrome, and Arista Flaws to KEV Catalog Amid Active Exploitation
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added three new vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The list of vulnerabilities is as follows – CVE-2026-20245 (CVSS score: 7.8) – An improper encoding or escaping of output vulnerability in Cisco Catalyst SD-WAN Manager that could allow…
AI, Global Security News, Risk Management
Drata brings visibility, control and auditability to enterprise AI agents
Drata has introduced AI Agent Governance, a new security category focused on managing the risks and oversight requirements of AI agents, while extending its trust platform to support enterprise adoption of autonomous AI systems. While McKinsey finds 57% of business leaders cite governance friction as the top blocker to deploying more AI, this move is…
AI, Cybersecurity, Exploits, Global Security News
Microsoft feud escalates as researcher drops new Windows zero-day
The long-running feud between Microsoft and security researcher Nightmare Eclipse has entered a new chapter. Eclipse, who has spent the past several months publicly releasing unpatched Windows vulnerabilities while sparring with Microsoft over vulnerability disclosure practices, has published exploit code for a new zero-day flaw dubbed RoguePlanet. The researcher said their exploit uses a race…
AI, Apps, Cybersecurity, Exploits, Global Security News, Network Security, Risk Management
U.S. CISA adds Cisco Catalyst SD-WAN, Arista Extensible Operating System (EOS), and Google Chromium V8 flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco Catalyst SD-WAN, Arista Extensible Operating System (EOS), and Google Chromium V8 flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added BerriAI LiteLLM and Check Point Security Gateway flaws to its Known Exploited Vulnerabilities (KEV) catalog. The two flaws added to…
Global Security News
Microsoft Patches Record 206 Flaws, Including Three Zero-Days and Critical RCE Bugs
Microsoft on Tuesday released fixes for a record 206 security vulnerabilities impacting its software portfolio, including three flaws that have been publicly disclosed at the time of release. Of the 206 flaws, 39 are rated Critical, and 167 are rated Important in severity. This includes 63 privilege escalation, 56 remote code execution, 30 information disclosure,…
AI, Apps, Exploits, Global Security News
F5 adds AI-powered threat detection and API security for on-premises environments
F5 has introduced new web application and API protection (WAAP) capabilities for its Application Delivery and Security Platform. The company said the updates are intended to address a threat landscape in which AI models can accelerate the time between vulnerability discovery and exploitation, giving attackers faster access to offensive capabilities. The new features expand the…
AI, Exploits, Global Security News
ServiceNow Flaw Exploited to Gain Unauthorized Access to Customer Instances
ServiceNow has warned about a security incident in which unknown threat actors exploited a flaw to obtain deeper unauthorized access to susceptible instances. “On June 5, 2026, ServiceNow applied a security update to hosted customer instances,” the company revealed in an advisory that requires customer access. “The update concerned a security issue that could allow…
AI, Exploits, Global Security News
Microsoft Defender RoguePlanet Zero-Day Grants SYSTEM Access on Updated Windows
The anonymous security researcher going by the name Chaotic Eclipse (aka Nightmare-Eclipse) has released a proof-of-concept (PoC) exploit for yet another Microsoft Defender zero-day named RoguePlanet. “The exploit is a race condition, so it’s a hit or miss,” the researcher, who published the exploit under a new GitHub account, “MSNightmare” said. “I have managed to…
AI, Global Security News, Risk Management
Cyber resilience metrics that drive action
In this Help Net Security video, Pete Bowers, COO at NormCyber, explains how organizations can build a cyber resilience metrics program that supports better decisions. He questions common ways of measuring resilience, such as risk registers, tool scores, and annual tests, and points out their limits. These methods often rely on opinion, narrow data, or…
AI, Apps, Compliance, Cybersecurity, Data Breaches, Exploits, Global Security News, Risk Management
Enterprises know AI-generated code is vulnerable; they’re shipping it anyway
AI-generated code is riddled with security flaws, yet enterprises are shipping more of it than ever before. Why? Perhaps they’re over-confident, lack true visibility into security risks, or are simply choosing to ignore the problem and hope it goes away. It’s a dangerous game to play at the dawn of the agentic AI era, as…
AI, Exploits, Global Security News
Microsoft Releases Record-Breaking Patch Tuesday With 208 CVEs
Microsoft Patch Tuesday security updates for June 2026 fix a record 208 CVEs, including one actively exploited zero-day and multiple critical RCE flaws. Microsoft Patch Tuesday security updates for June 2026 mark a record. Microsoft shipped fixes for 208 CVEs across Windows, Office, Azure, Exchange, Hyper-V, Secure Boot, BitLocker, and a range of AI tooling.…
AI, Global Security News
Rubrik enhances data security with AI agents and autonomous recovery
Rubrik introduced Rubrik AI, an agent-first interface for its Security Cloud and Agent Cloud, allowing customers to define business outcomes that the software executes by reasoning over data, identities, and deployed agents.
Global Security News
Windows 10 KB5094127 update fixes vulnerabilities, enhances Secure Boot monitoring
The KB5094127 update primarily focuses on security enhancements and bug fixes, as Microsoft is no longer introducing new features to Windows 10.
AI, Exploits, Global Security News, malware
A Record-Breaking Patch Tuesday for June 2026
Microsoft today released software updates to plug nearly 200 security holes across its Windows operating systems and supported software, a record number of fixes for the company’s monthly Patch Tuesday cycle. Nearly three dozen of those bugs earned Microsoft’s most dire “critical” rating, and exploit code for at least three of the weaknesses is now…
Endpoint, Exploits, Global Security News
ServiceNow discloses security incident exposing customer data
ServiceNow is warning about a security incident after attackers exploited an unauthenticated access flaw through a vulnerable API endpoint, allowing them to query data from customer instances. […]
Global Security News
SAP fixes critical flaws in NetWeaver and Commerce Cloud
SAP has released fixes for 15 vulnerabilities as part of its June 2026 Security Patch package, including four critical-severity flaws affecting SAP NetWeaver and SAP Commerce Cloud. […]
Global Security News
Microsoft releases Windows 10 KB5094127 extended security update
Microsoft has released the Windows 10 KB5094127 extended security update, which fixes the June 2026 Patch Tuesday vulnerabilities and adds new functionality to monitor the rollout of updated Secure Boot certificates that replace those expiring this month. […]
Global Security News
Microsoft June 2026 Patch Tuesday fixes 3 zero-day, 200 flaws
Today is Microsoft’s June 2026 Patch Tuesday, with security updates for 200 flaws and three publicly disclosed zero-day vulnerabilities. […]
AI, Apps, Cybersecurity, Exploits, Global Security News, Network Security, Risk Management
Rubrik Brings Claude-Focused Tooling, Partner Program to Market
Rubrik, a security and AI operations company, has announced a new partner program and enhancements to bolster AI resilience and recovery. Rubrik Agent Cloud for Anthropic’s Claude Code and Claude Cowork will enable organizations to deploy Claude-powered agents at scale with observability, control, and agent rewind. Rubrik’s new cross-platform Rubrik AI automates and accelerates response…
Global Security News
E-Signature Security Checklist Before Selecting an E-Signature Tool
Electronic signature security starts before the first document is sent. A company needs to know how files are…
AI, Global Security News
Veeam Backup & Replication RCE Flaw Lets Domain Users Run Remote Code
Veeam has released security patches to address a critical flaw in its Backup & Replication software that could result in remote code execution. Tracked as CVE-2026-44963, the vulnerability carries a CVSS score of 9.4 out of a maximum of 10.0. “A vulnerability allowing remote code execution (RCE) on the Backup Server by an authenticated domain…
Compliance, Global Security News
75% of Firms Deploy Vulnerable Code Amid Pressure on CISOs, Report Finds
Checkmarx report warns that business pressure is among the reason security leaders let security compliance slip
AI, Exploits, Global Security News
New Veeam vulnerability exposes backup servers to RCE attacks
Veeam has released security updates to patch a critical Backup & Replication security flaw that can be exploited to gain remote code execution (RCE) on domain-joined backup servers. […]
AI, Exploits, Global Security News, Russia
WinRAR Flaw Exploited by Russia-Aligned Groups to Deploy Stealers in Ukraine
Two Russia-aligned cyber attack campaigns have continued to exploit a security flaw in WinRAR to target Ukrainian organisations, almost a year after patches for the vulnerability were released. The activity has been attributed by Trend Micro to Earth Dahu (aka Gamaredon) and SHADOW-EARTH-066 (aka UAC-0226). It involves the exploitation of CVE-2025-8088, a path traversal flaw…
Global Security News, Network Security
Cisco SASE with Meraki: Get in the Fast Lane to SASE
Simplify your security with Cisco SASE with Meraki. Easily integrate SD-WAN with SSE for fast, automated protection across your hybrid network.
Exploits, Global Security News
Chrome V8 Zero-Day CVE-2026-11645 Exploited in the Wild – Patch Now
Google has released security updates to address 74 vulnerabilities, including one that has come under active exploitation in the wild. The high-severity vulnerability, tracked as CVE-2026-11645 (CVSS score: 8.8), has been described as an out-of-bounds memory access in V8, Chrome’s JavaScript and WebAssembly engine. “Out-of-bounds read and write in V8 in Google Chrome prior to…
AI, Apps, Cybersecurity, Global Security News, Network Security, Risk Management
NetRise Builds New Partner Program for MSSPs, VARs, More
Security company NetRise is abandoning the go-it-alone strategy in its war against hidden software vulnerabilities. The Austin, Texas-based software supply chain security specialist announced the rollout of its new Discovery Partner Program today. NetRise bets on the channel to scale software risk management The initiative is a deliberate shift toward a partner-first business model, aiming…
AI, Apps, Cybersecurity, Endpoint, Exploits, Global Security News, Network Security, Risk Management
U.S. CISA adds BerriAI LiteLLM and Check Point Security Gateway flaws to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds BerriAI LiteLLM and Check Point Security Gateway flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added BerriAI LiteLLM and Check Point Security Gateway flaws to its Known Exploited Vulnerabilities (KEV) catalog. The two flaws added to the catalog are: CVE-2026-42271 (CVSS score…
AI, Cybersecurity, Exploits, Global Security News
LiteLLM Flaw CVE-2026-42271 Exploited in the Wild, Chains to Unauthenticated RCE
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a high-severity flaw impacting BerriAI LiteLLM to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerability, tracked as CVE-2026-42271 (CVSS score: 8.7), is a command injection vulnerability that could allow any authenticated user to run arbitrary commands on the
AI, Global Security News, Risk Management
Treating AI agents like service accounts for federated query security
In this interview with Help Net Security, Paras Malhotra, CISO at Starburst, explains how the company handles data governance across federated query environments. Topics include layering Starburst’s access controls above native source permissions, tiering vendor risk across more than 200 partners and connectors, and building audit trails for autonomous agents. The conversation covers how AIDA…
AI, Global Security News, malware
Malware ships with bugs that defenders could use against it
Static analysis tools have spent years scanning legitimate software for security bugs before it goes out the door. The same scanners work on malware, and malware carries a steady supply of its own bugs. Researchers ran four of these tools across 658 leaked malware projects and found that close to 90 percent contained at least…
AI, Apps, Cybersecurity, Global Security News
Cybersecurity jobs available right now: June 9, 2026
Application Security Architect INTENSITY Global Group | Israel | Hybrid – View job details As an Application Security Architect, you will design secure application architectures, perform threat modeling and security assessments, define security standards and controls, integrate security into the SDLC and CI/CD pipelines, support application security tooling and incident response, and guide engineering teams…
Global Security News
Ubiquiti UniFi OS server vulnerabilities allow unauthenticated remote code execution
The security flaws, tracked as CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910, were addressed in May and impacted UniFi OS Server versions 5.0.6 and earlier.
AI, Apps, Compliance, Endpoint, Global Security News, Network Security, Risk Management, Venture
ICYMI: May 2026 @AWS Security
Read all about the latest AWS security features, compliance updates, and hands-on resources in our new, monthly digest posts. You’ll find expert blog posts, new service capabilities, code samples, and workshops. AWS Security Blog posts This month’s AWS Security Blog posts covered AI security, network protection, identity management, compliance frameworks, and supply chain security. Read…
AI, Exploits, Global Security News
One-Character Linux Kernel Flaw Enables Local Root Access, Exploits Now Public
Security researchers have published a detailed, working exploit for a Linux kernel use-after-free that lets an unprivileged local user escalate to root and break out of a container. The flaw, CVE-2026-23111, sits in the kernel’s nf_tables packet-filtering code and was patched upstream on February 5, 2026. Exodus Intelligence released its full technical walkthrough on June…
AI, Apps, Global Security News, Risk Management, Venture
Minimus Unveils New Supply Chain Protection Proxy and Command-Line Interface for Container Management
Cloud software security firm Minimus today expanded its product portfolio with the general availability of Minimus Supply Chain Protection and minicli. The tools introduce a unified approach to managing third-party software risks and container image configurations. The release of Supply Chain Protection directly targets vulnerabilities found within the application package universe, where interwoven dependencies are…
Global Security News
Gogs patches critical zero-day enabling remote code execution
Gogs has patched a critical security zero-day flaw that can allow attackers to compromise Internet-facing instances and access any repositories (including private ones). […]
AI, Apps, Cloud Security, Compliance, Cybersecurity, Data Breaches, Endpoint, Global Security News, malware, Network Security, Risk Management
Operationalizing AWS security: A maturity roadmap
Enabling security tooling is the starting point. Making it operational—where findings drive decisions, response times are measurable, and your security posture improves week over week—is where most organizations struggle. This blog post provides a phased maturity roadmap for organizations that have already enabled AWS Security Hub and Amazon GuardDuty. These two services form the foundation…
AI, Global Security News
Guardrails for agents: How to secure AI at runtime
Here’s how identity security is becoming the enforcement layer for agentic AI.
AI, Global Security News
Reducing security operations complexity with Wazuh Cloud
Security teams are increasingly overwhelmed by alert fatigue, infrastructure maintenance, and complex hybrid environments. This article explores how Wazuh Cloud helps simplify SIEM/XDR operations through managed infrastructure, automated scaling, and AI-driven security analysis. […]
Cybersecurity, Exploits, Global Security News
Check Point links VPN zero-day attacks to Qilin ransomware gang
Israeli cybersecurity company Check Point has released security updates to patch a critical flaw affecting Remote Access VPN and Mobile Access deployments, which was exploited in zero-day attacks. […]
AI, Global Security News, Risk Management
Silverfort Securing AI Agents With Copilot Studio Integration
Identity security organization Silverfort has announced it will integrate its Identity Security control for AI agents into Microsoft Copilot Studio. Runtime security addresses Copilot actions before execution The integration will enable Silverfort to deliver inline identity security at runtime, enforcing intelligent access control policies the moment a Copilot agent attempts to act, blocking unauthorized access…
AI, Exploits, Global Security News, Risk Management
RidgeBot 7.0 automates Active Directory attack simulations for security validation
Ridge Security has announced the release of RidgeBot 7.0, an update to its automated security validation platform that introduces automated Windows Active Directory penetration testing capabilities. The new version enables organizations to conduct end-to-end domain compromise simulations, helping security teams identify attack paths and prioritize exploitable risks. RidgeBot 7.0 delivers automated Active Directory penetration testing…
AI, Apps, Cybersecurity, Data Breaches, Exploits, Global Security News, Network Security, Risk Management
15 tough cybersecurity questions every CISO must answer
As CISOs know, an effective security program cannot be static. Rather, it must adapt to the evolving threat landscape and an ever-changing business environment. To adapt and improve, CISOs must continuously evaluate their existing program. That starts with asking tough questions about their performance, investments, and strategies. Here, security leaders share 15 questions every CISO…
AI, Global Security News, Risk Management
OpenAI is locking down parts of ChatGPT to reduce data theft risks
OpenAI has started rolling out Lockdown Mode for ChatGPT, an optional security setting that restricts access to external resources and several product capabilities. It is available for personal accounts, including Free, Go, Plus, and Pro plans, as well as self-serve ChatGPT Business accounts. “Lockdown Mode is not intended for everyone. It is designed for people…
AI, Global Security News
DockSec: Open-source AI-powered Docker security scanner
DockSec is an OWASP Incubator Project that combines three container security scanners with a language-model layer for explanation and remediation. Created by Advait Patel, the Python tool runs Trivy, Hadolint, and Docker Scout against a developer’s Dockerfile and image, correlates the findings, returns a 0-100 security score, and proposes line-specific fixes. DockSec requires Python 3.12…
AI, Global Security News
When attacks spread too far: Lessons from real cyber attack case studies
In this Help Net Security video, Michael Adjei, Director, Systems Engineering at Illumio, explains three real world cyber attacks and what went wrong during detection. Adjei walks through a collaboration tool scam that copied Microsoft Teams, an identity phishing case used for payment fraud, and a long running advanced threat campaign. Each story follows the…
AI, Global Security News, Network Security
52% of direct-to-IP threats are missing from intelligence feeds
Security tools are good at inspecting websites, domains, URLs, and files, so attackers are moving lower in the stack and communicating directly with IP addresses, where visibility is limited. According to Palo Alto Networks’ report, this creates a visibility gap that allows malicious traffic to blend into normal internet activity and evade detection. At the…
AI, china, Cybersecurity, Global Security News, malware, Network Security
SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 100
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Malware Targeting WordPress Abuses Steam Community Profiles for Command & Control Operations Legitimate-Looking Codex Remote UI Secretly Steals Your AI Tokens Operation Dragon Weave : Uncovering a China-Linked Campaign Targeting Czech Republic and Taiwan…
AI, china, Cybersecurity, Data Breaches, Exploits, Global Security News, Government & Policy, malware, Network Security, privacy, Risk Management, Russia
Security Affairs newsletter Round 580 by Pierluigi Paganini – INTERNATIONAL EDITION
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. U.S. CISA adds SolarWinds Serv-U flaw to its Known Exploited Vulnerabilities catalog Report: Anthropic Deploys Engineers…
AI, Cybersecurity, Exploits, Global Security News, Network Security, Risk Management
U.S. CISA adds SolarWinds Serv-U flaw to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds SolarWinds Serv-U flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added SolarWinds Serv-U flaw, tracked as CVE-2026-28318 (CVSS ver 3.1 score of 7.5), to its Known Exploited Vulnerabilities (KEV) catalog. SolarWinds Serv-U is a managed file transfer (MFT) and secure file…
Cybersecurity, Exploits, Global Security News
CISA Adds Actively Exploited SolarWinds Serv-U DoS Flaw to KEV Catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a high-severity security flaw impacting SolarWinds Serv-U multi-protocol file server software to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The vulnerability, tracked as CVE-2026-28318 (CVSS score: 7.5), is a denial-of-service (DoS) bug that causes the service to crash
AI, Global Security News
AI Agent Uncovers 21 Zero-Days in FFmpeg; Chrome Patches Record 429 Bugs
Two things landed within days of each other this week. A security startup reported 21 previously unknown vulnerabilities in FFmpeg, the media library inside almost everything that touches video, all of them found by an autonomous AI agent. The same week, Google shipped Chrome 149 with patches for 429 security bugs, the most ever in…
Exploits, Global Security News, Government & Policy
Cisco Catalyst SD-WAN Manager CVE-2026-20245 Flaw Actively Exploited – No Patch Available
Cisco has warned that a high-severity security flaw impacting Catalyst SD-WAN Manager has come under active exploitation. The vulnerability, tracked as CVE-2026-20245, carries a CVSS score of 7.8 out of a maximum of 10.0. It affects the following deployment types – On-Prem Deployment Cisco SD-WAN Cloud-Pro Cisco SD-WAN Cloud (Cisco Managed) Cisco SD-WAN for Government…
AI, Apps, Cloud Security, Endpoint, Global Security News
Building secure B2C applications with fine-grained access control using Amazon Cognito and Amazon Verified Permissions
Modern web applications require robust security controls to protect user data and application resources. Authentication and authorization are two fundamental pillars of application security that answer critical questions: Who are you? and What are you allowed to do? Implementing these controls correctly can be challenging for developers, especially when building data-intensive applications with frameworks like…
AI, Global Security News
Infosecurity Europe: OWASP Introduces Agentic AI Security Maturity Framework
The OWASP agentic AI security framework helps organizations assess governance maturity vs adoption and adjust governance as needed
AI, Global Security News, Risk Management
Infosecurity Europe: AI Coding Tools Need Built-In Security for Agentic Development Era
Ox Security field CTO, Boaz Barzel, makes the case for vibe security to tackle AI agent coding risks
Exploits, Global Security News
Hackers Exploit Critical Everest Forms Pro WordPress Plugin Flaw to Take Over Sites
Threat actors are actively exploiting a critical security flaw in Everest Forms Pro, a WordPress plugin with about 4,000 active installations, to execute arbitrary code, leading to a complete site compromise. The vulnerability in question is CVE-2026-3300 (CVSS score: 9.8), a remote code execution bug impacting all versions of the plugin up to, and including,…
AI, Global Security News, malware
FIFA World Cup 2026 Scams Are Already Live: Fake Sites, Banking Malware, and Stolen Logins
Security researchers and the FBI are warning that a wave of FIFA-themed fraud is already hitting World Cup 2026 fans, days before the June 11 kickoff. Recent reports describe thousands of lookalike FIFA domains, banking malware hidden inside pirate streaming apps, and at least one operation that copies FIFA’s login page well enough to take…
AI, Global Security News, Risk Management
AI agent governance gets harder when agents outnumber your people
In this Help Net Security video, Amit Gautam, CTO at Abluva, explains the security risks that autonomous AI agents bring into enterprise environments. He opens with a real case: a reconciliation agent at a financial services firm had legitimate access to a customer database. A poison instruction from upstream changed its behavior, and it scanned…
Global Security News
Offroad launches with $7 million to use AI agents for identity security
Offroad addresses the growing complexity of identity security, which has surpassed manual review capabilities.
AI, china, Cybersecurity, Funding, Global Security News, Government & Policy
Hill Dems hammer GOP for $250M CISA budget cut
House Democrats criticized a draft Republican Department of Homeland Security spending bill Thursday that they said would cut funding for the Cybersecurity and Infrastructure Security Agency by $250 million. Republicans said the bill provides $2.4 billion for CISA, and that among its focuses are “improving cybersecurity resilience,” in the words of House Appropriations Chairman Tom…
AI, Global Security News, Network Security
Video: What Partners Need to Know About Cisco Cloud Control
Cisco has launched Cisco Cloud Control, a new platform designed to manage networking, security, observability, compute, and collaboration from a single interface. But the bigger story is Cisco’s vision for AgenticOps—an operating model where AI agents help investigate issues, correlate data, recommend actions, and eventually automate IT operations. In this video, we break down what…
AI, Cybersecurity, Exploits, Global Security News, Network Security, Risk Management
U.S. CISA adds Mirasvit Full Page Cache Warmer flaw to its Known Exploited Vulnerabilities catalog
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Mirasvit Full Page Cache Warmer flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Mirasvit Full Page Cache Warmer flaw, tracked as CVE-2026-45247 (CVSS ver 4.0 score of 9.3), to its Known Exploited Vulnerabilities (KEV) catalog. The CVE-2026-45247 flaw is a…