
eCrime Actor Activity
- PUNK SPIDER: Used AI-generated scripts to accelerate credential dumping and erase forensic evidence, demonstrating how adversarial prompt engineering can automate post-exploitation operations.
- ALTERED SPIDER: Compromised more than 300 software dependencies in a single day to harvest credentials and pivot into cloud environments.
3. Falcon Guardian — Technical Architecture Deep Dive
Core Capabilities
| Capability | Description |
|---|---|
| AI Agent Discovery & Inventory | Continuously discovers known and shadow AI agents across Windows, macOS, Linux endpoints. Identifies deployment origin, usage patterns, and security status. |
| Agent Runtime Visibility | Connects AI agent behavior directly to Falcon endpoint telemetry; establishes a causal chain from user prompt → identity → tool call → skill use → downstream system action. Full execution graph visibility. |
| Agent Access Controls | Defines which AI agent types are permitted to run on managed endpoints. Blocks unauthorized agents and translates governance policy into enforceable runtime controls. |
| Runtime Detection & Response | Detects attacks on agents and malicious behavior; reconstructs full execution chains; determines blast radius in real time; contains threats before they spread. |
| AI Gateway (Pre-Beta) | Centralized control point for enterprise AI traffic with consistent visibility and policy enforcement across supported models and services. Context-aware using user, agent, endpoint, identity, asset, and security posture signals. |
| Falcon Complete for Guardian | 24/7 expert-led detection, investigation, response (MDR) specifically tuned to AI agent threats. Elite analysts assess intent, distinguish legitimate vs malicious behavior, stop threats before impact. Available Q3 2026. |
| Adversary OverWatch Cross-Domain | Extends managed cross-domain threat hunting to AI agents using runtime context from Guardian. Expert hunters combine behavioral context with frontline adversary tradecraft. |
Architecture Diagram
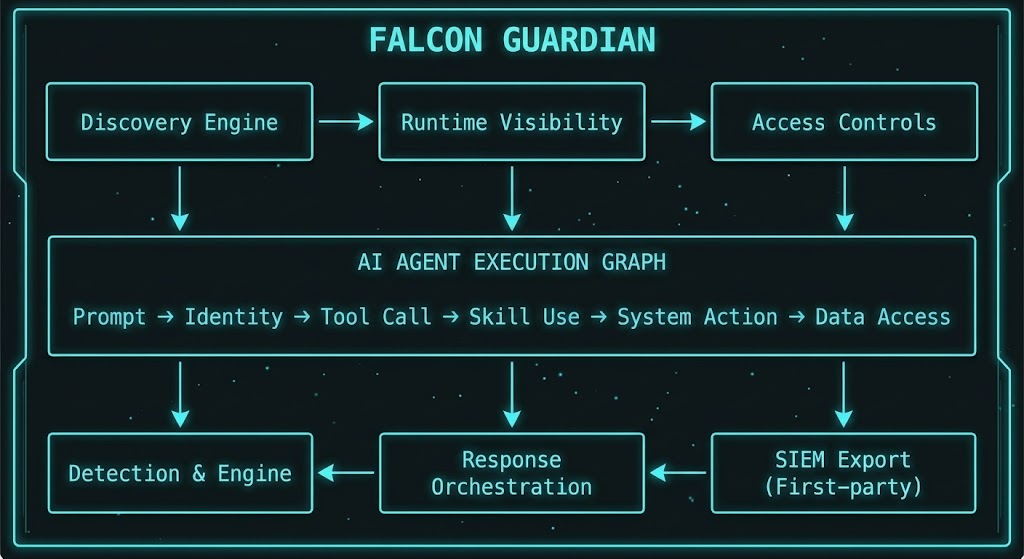
Key Design Decisions:
- Endpoint-first architecture — unlike governance-only solutions that sit above the agent, Falcon Guardian operates at runtime where agents execute
- Causal chain tracing — every action is connected back to its originating prompt through identity, tool call, skill use, and system action
- First-party data model — agent telemetry ingested as first-party data into Next-Gen SIEM eliminates third-party ingest costs that scale linearly with agent volume (potentially millions annually for large enterprises)
Security Cloud Integration
Falcon Guardian leverages the CrowdStrike Security Cloud and world-class AI for:
- Real-time indicators of attack (IOAs)
- Threat intelligence on adversarial prompting techniques
- Evolving adversary tradecraft patterns
- Enriched telemetry from across the enterprise endpoint estate
SIEM Integration — First-Party Data Model
Critical Differentiator: Falcon Guardian treats agent telemetry as first-party data, eliminating third-party ingest costs that scale linearly with agent volume. For a large enterprise running hundreds of AI agents, competitors’ bolt-on approaches can cost millions annually in third-party SIEM ingest fees. Falcon Guardian’s native integration includes default retention for compliance-ready visibility into AI agent activity.
Certified Pipeline Approach
Detection at the Edge: Third-party data sources arrive detection-ready through pre-built, pre-tested flows that run detection logic at the edge before data reaches its destination. This reduces MTTD and eliminates pipeline overhead — a key architectural decision that competitors cannot easily replicate.
4. The Agentic SOC
What Is the Agentic SOC?
A production operating model where expert AI agents and human analysts operate as one unified system. It represents CrowdStrike’s next evolution of security operations, combining platform-native telemetry with coordinated specialist agents.
Key Capabilities
| Capability | Status | Description |
|---|---|---|
| Unified Foundation (Pre-Beta) | Pre-beta | Third-party data arrives detection-ready through certified pipelines. Detection logic runs inside the pipeline at the edge before data reaches its destination, reducing MTTD and eliminating pipeline overhead. |
| Coordinated Teams of Specialist Agents | GA | Fleets of battle-tested agents, built by CrowdStrike experts and coordinated by an orchestrator agent, work out-of-the-box for cross-domain investigations, proactive reconnaissance, digital risk protection, cloud security monitoring. |
| Agentic Investigations with Shared Context (Pre-Beta) | Pre-beta | When detections warrant investigation, an orchestrator summons specialist agents across every associated domain and data source in parallel. They build on each other’s findings through a shared context layer that learns continuously from global detections (millions of incidents worldwide) and local customer environments. Converges on a single verdict — clearing queues or escalating with pre-assembled context for human review. |
| Agentic Recon (Public Preview) | Public preview | Intelligence agents continuously investigate threats across the open, deep, and dark web using natural language queries. They assess related findings and impact, then recommend mitigation actions — moving teams from manual triage to continuous exposure management before adversaries can leverage them. |
| Hybrid Analysis, Reengineered (Public) | Public | The community malware analysis tool now offers API-first access with an open-source MCP server, enabling direct plug-in into AI agent workflows for file-based threat intel enrichment. |
Learning Loops — How the Agentic SOC Compounds Intelligence
The agentic SOC compounds intelligence through two compounding loops:
- Global loop: Agents are informed by millions of real detections from around the world and get sharper with every incident the Falcon Complete team stops.
- Local loop: The same shared context layer that agents reason over during an investigation is where their learning accumulates. Every decision, correction, and resolution in a customer’s environment is collected there — unique to that organization and accessible to all of its CrowdStrike agents.
Unified Agentic SOAR Workspace (Public Preview)
A new interface converges Charlotte AI AgentWorks, SOAR orchestration, and Falcon Foundry in a single UI:
- For each workflow, teams define triggers, data sources, conditions, agents to invoke, and actions to take.
- Teams set what is fully automated vs requires human approval.
- Connects to tools of their choice via CrowdStrike-managed MCP servers.
“Bring Your Own Model” (GA)
Teams can use existing OpenAI and Anthropic licenses to match the right AI model to each job — optimizing for reasoning complexity, latency, or cost. This enables a more flexible and economical way to build, test, and run agents without being locked into a single provider.
“Connect to Any Tool, Any Agent” (GA)
Third-party agents can connect into Falcon tools through a CrowdStrike-managed MCP server, while Charlotte AI AgentWorks agents can reach out to the tools and data that security teams already run. The existing stack automatically becomes part of the agentic SOC — no overhaul required.
5. Sponsors & Ecosystem Partners
Event Statistics
| Metric | Value |
|---|---|
| Total Attendees | 10,000+ |
| Sessions Delivered | 500+ |
| Ecosystem Sponsors | 150+ |
| Countries Represented | 40+ (per attendee survey) |
Premier Sponsors
| Sponsor | Focus Area |
|---|---|
| Amazon Web Services (AWS) | Cloud security, Zero Trust infrastructure |
| Accenture | Managed detection and response, AI governance services |
| Anthropic | LLM safety, prompt injection defenses, constitutional AI |
| Dell Technologies | Endpoint hardware, TPM 2.0+ security foundations |
| Ernst & Young LLP (EY US) | Risk advisory, compliance frameworks for AI systems |
Diamond Sponsors
| Sponsor | Focus Area |
|---|---|
| Google Cloud | Container security, GCP-native threat detection |
| Kroll | Threat intelligence, fraud prevention, AML |
| Mimecast | Email security, phishing defense, BEC protection |
| NVIDIA | AI infrastructure, secure compute environments |
| Okta | Identity and access management, zero trust identity |
| Rubrik | Data protection, immutability for ransomware defense |
| Zscaler | Cloud Zero Trust, SASE architecture |
Sponsor Ecosystem Insight
The mix of sponsors reflects the cloud-native, model-centric nature of modern AI security workloads:
- Premier sponsor presence from AWS and Anthropic demonstrates strong alignment with infrastructure providers and LLM safety companies.
- Diamond sponsor diversity (Okta for identity, Mimecast for email, Rubrik for data protection) shows that cross-domain coverage is a market expectation — no single vendor can own the entire attack surface.
6. Competitive Landscape
| Vendor | AIDR Approach | Differentiation |
|---|---|---|
| CrowdStrike | Endpoint runtime enforcement with full causal chain tracing. Native SIEM integration, agentic SOC, certified pipelines. First-party data model eliminates pipeline overhead; agentic SOC compounds intelligence through global and local learning loops. Platform-native approach creates high switching cost. | |
| Palo Alto Networks | Cloud-native agent governance with strong container security integration. Deep cloud infrastructure integration (Kubernetes, service meshes). Strong container runtime protection. | |
| Microsoft Defender | Integrated with Azure AI services and Office 365. Deep Windows/Office 365 integration. Native LLM telemetry from Microsoft Fabric Copilot. | |
| SentinelOne | Autonomous endpoint response with self-healing architecture. Agentless deployment model. Self-healing without human intervention. | |
| Wiz | Cloud-native AI observability and infrastructure-as-code scanning for LLM deployments. Infrastructure security focus. Container registry scanning, model provenance verification. |
CrowdStrike’s Moat
The unified agentic SOC combines:
- Platform-native telemetry (no pipeline overhead)
- Coordinated specialist agents working from a shared context layer that learns continuously
- Expert-led response through Falcon Complete MDR
- First-party data model eliminating costly bolt-on architectures
For a large enterprise running hundreds of AI agents, the first-party data model alone eliminates millions in annual third-party SIEM ingest costs. The learning loops compound over time in ways competitors cannot easily replicate without similar platform depth.
7. Key Takeaways Summary
Technical
- Falcon Guardian provides complete runtime security for AI agents with discovery, visibility, access control, and threat detection/response in one unified product.
- The agentic SOC uses coordinated specialist agents working from a shared context layer that learns continuously from global detections (millions of incidents) and local customer environments.
- Certified pipelines eliminate third-party data pipeline overhead — detection runs at the edge before data reaches its destination, reducing MTTD.
- Native SIEM integration treats agent telemetry as first-party data with default retention for compliance-ready visibility — eliminating costly bolt-on architectures.
Strategic
- AI has changed attack speed (breakout time: 29 minutes) but not fundamentally changed adversary intent — runtime enforcement is now non-negotiable.
- The endpoint remains the control point for stopping attacks, even in an agentic world where agents execute system-level actions autonomously.
- Shadow AI discovery must be continuous and automated — governance alone cannot stop already-executing threats.
Market
- 150+ ecosystem sponsors indicate strong vendor alignment around securing the AI revolution.
- Premier sponsor mix (AWS, Anthropic, NVIDIA) reflects cloud-native, model-centric nature of modern AI security workloads.
- Diamond sponsor diversity (Okta, Mimecast, Rubrik) shows cross-domain coverage is a market expectation — no single vendor can own the entire attack surface.
Bottom Line: Fal.Con 2026 demonstrated that the cybersecurity industry has reached an inflection point. CrowdStrike’s Falcon Guardian provides complete visibility and control at the endpoint where autonomous agents execute, with native SIEM integration, agentic investigation teams, and certified third-party data pipelines. The threat landscape shows AI-enabled attacks up 89% year-over-year with breakout times down to just 27 seconds. CISOs must shift from posture-based security to runtime enforcement — or risk being unable to stop threats already in motion.
Appendix A: Key Quotes from Event
“AI hasn’t changed the attack, it has changed its speed.”
— George Kurtz, CEO & Founder, CrowdStrike
“The endpoint is where agents execute and across the enterprise. Governance alone can’t stop an agent already in motion.”
— George Kurtz
“Breakout time is the clearest signal of how intrusion has changed: 29 minutes on average, with the fastest recorded at 27 seconds.”
— Adam Meyers, Head of Counter Adversary Operations, CrowdStrike
Appendix B: Resources & Further Reading
- Falcon Guardian Product Page: https://www.crowdstrike.com/en-us/platform/falcon-guardian-aidr/
- 2026 Global Threat Report: https://www.crowdstrike.com/en-us/resources/reports/global-threat-report/
- Agentic SOC Documentation: https://www.crowdstrike.com/en-us/blog/crowdstrikes-next-generation-agentic-soc/
Report compiled from official CrowdStrike press releases, keynote recordings, and conference materials. Fal.Con 2026 — Las Vegas, September 2026.